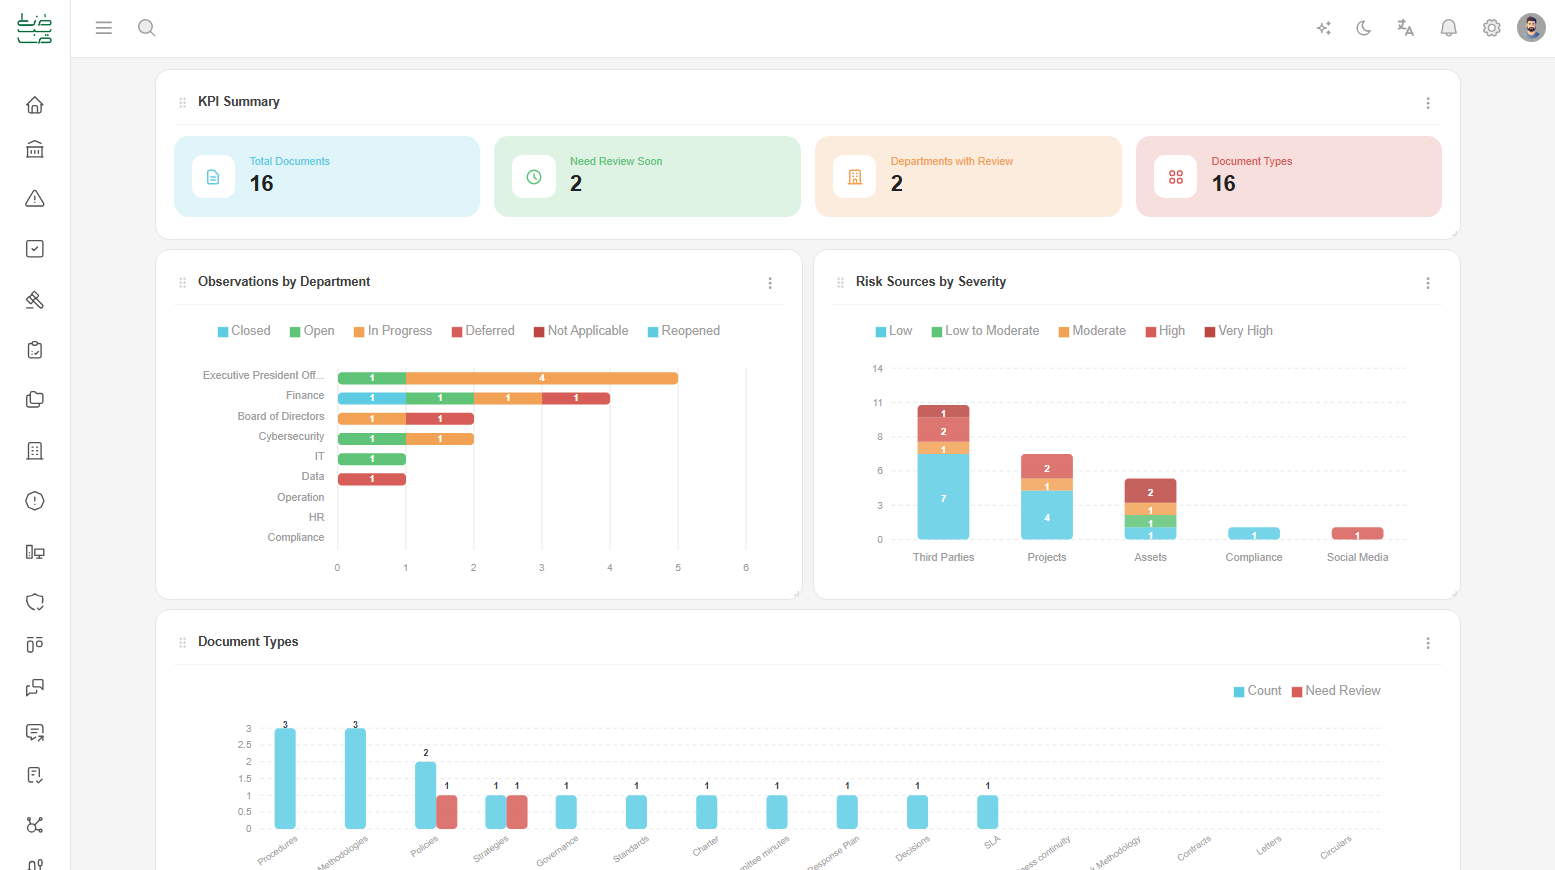
Cybersecurity Gets Complicated. We Make It Clear.
Frameworks. Risks. Audits. Vulnerabilities. Policies. Evidence. Regulators. Different teams. Different priorities.
The challenge isn't simply having more controls or producing more documents.


Frameworks. Risks. Audits. Vulnerabilities. Policies. Evidence. Regulators. Different teams. Different priorities.
The challenge isn't simply having more controls or producing more documents.
We help organizations understand their current cybersecurity posture, identify what needs attention, build the right capabilities, and continuously improve.
Beyond passing audits, we strengthen your cybersecurity while meeting regulatory and compliance requirements.
We start by understanding your organization, environment, business priorities, regulatory obligations, and current cybersecurity posture.
We identify gaps, risks, vulnerabilities, and areas that require improvement.
Not everything has the same level of risk. We help you focus resources on what matters most.
We work with your team to strengthen controls, processes, technologies, documentation, and cybersecurity capabilities.
We track progress, maturity, risks, compliance, and performance to give management a clear view of where the organization stands.
Cybersecurity doesn't stop when the project ends. We help you maintain visibility, continuously improve, and stay ready for regulatory reviews and audits.
We care about the smallest details to make your facility safe.