Cybersecurity Maturity Assessment
Rate the maturity of each control on the framework you work with, using an evidence-based scale, so you know where you stand today, where the gaps are, and how the level changes from one assessment to the next.
Made for: CISO, Cybersecurity Program Lead, GRC Team
Sounds familiar?
The team is asked for a maturity level, and the answer comes from each manager's impression of their own area. When someone asks what evidence supports the level, or how much has improved since the last assessment, there is nothing to show.
Each manager rates the level their own way, so departments cannot be compared.
Nothing shows what proves that a control has reached that level.
The plan lives in another file, and nobody can tell which control it will improve.
How MUNTABIQ helps
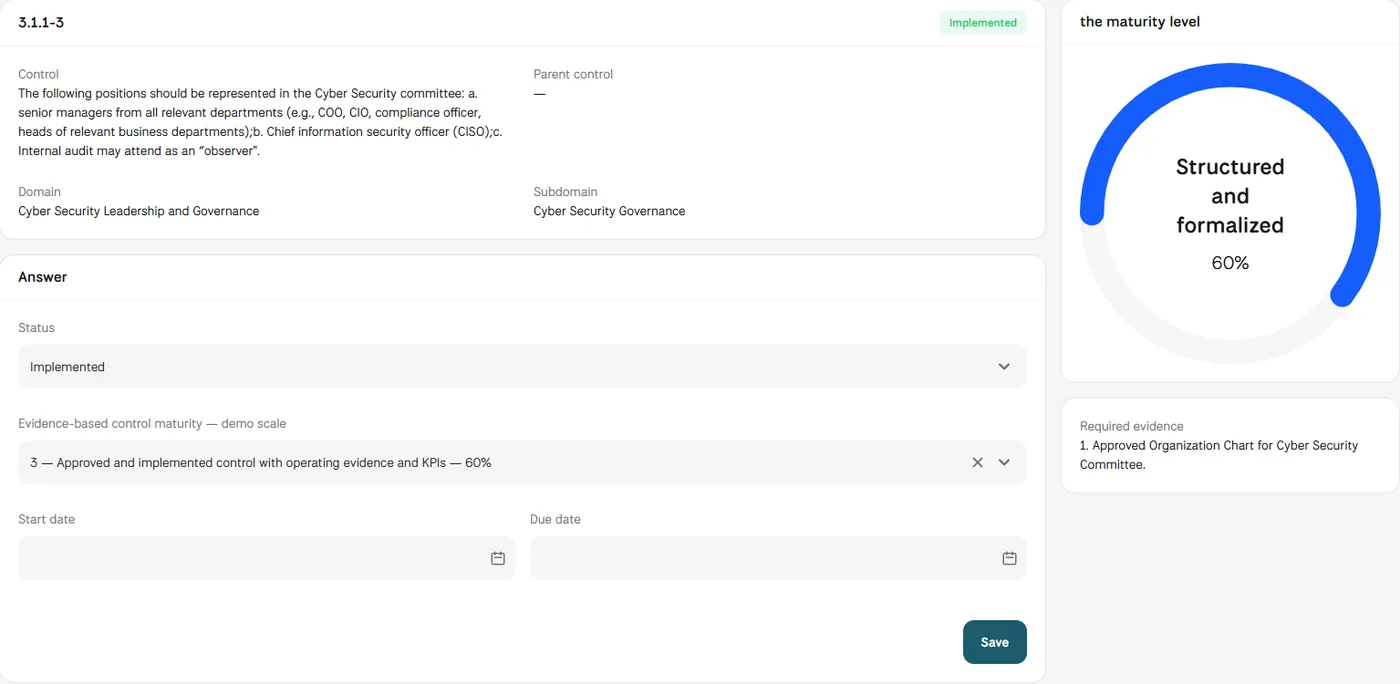
In MUNTABIQ, maturity is assessed inside the compliance assessment itself. Every control in the framework has its text, domain and required evidence, and the owner selects the implementation status and an evidence-based maturity level from a graded scale, shown on a dial on the control page. The scale and its level descriptions are set up with you, and the compliance dashboard shows maturity levels and average maturity over time for each framework.
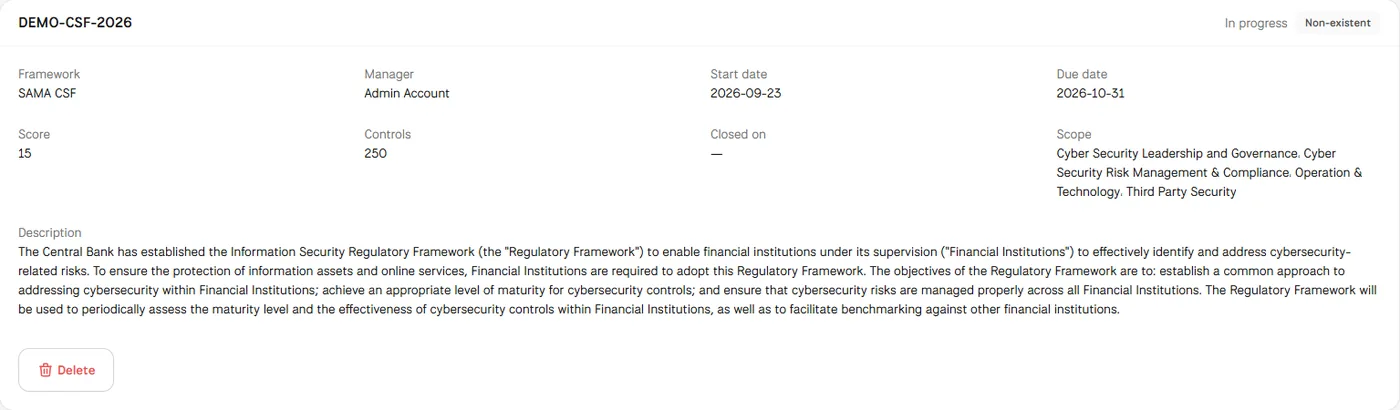
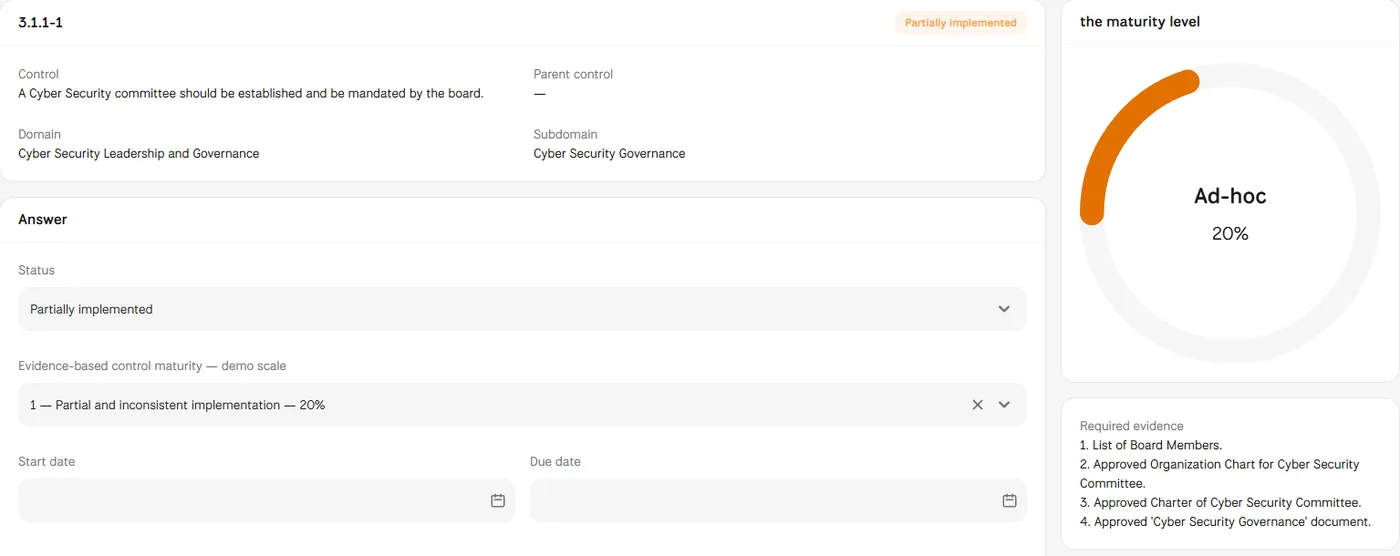
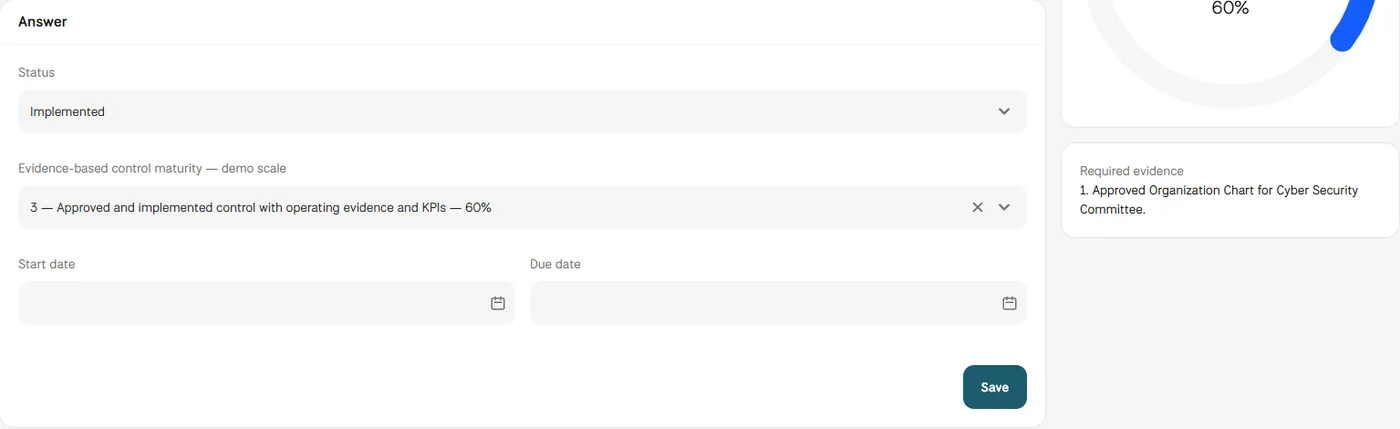
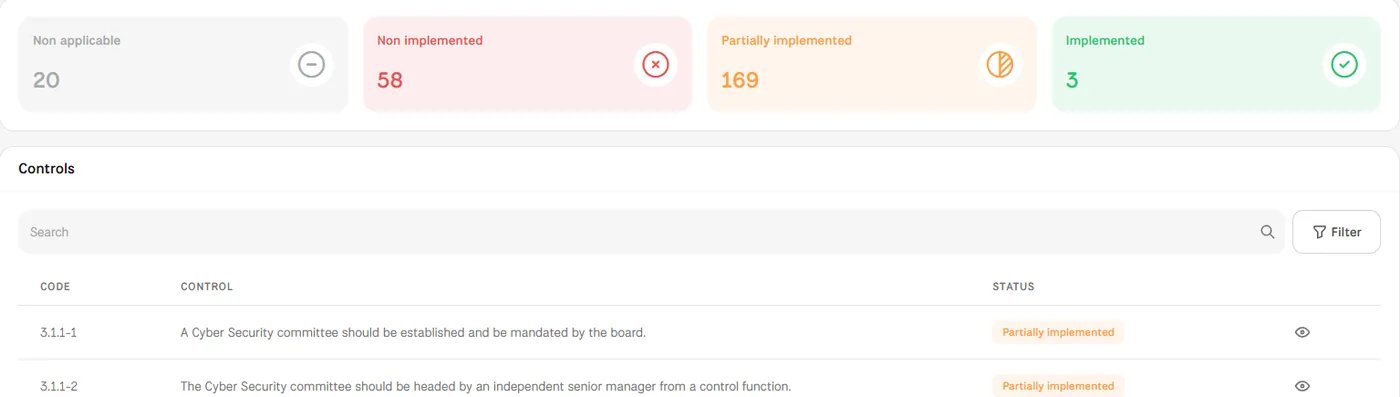
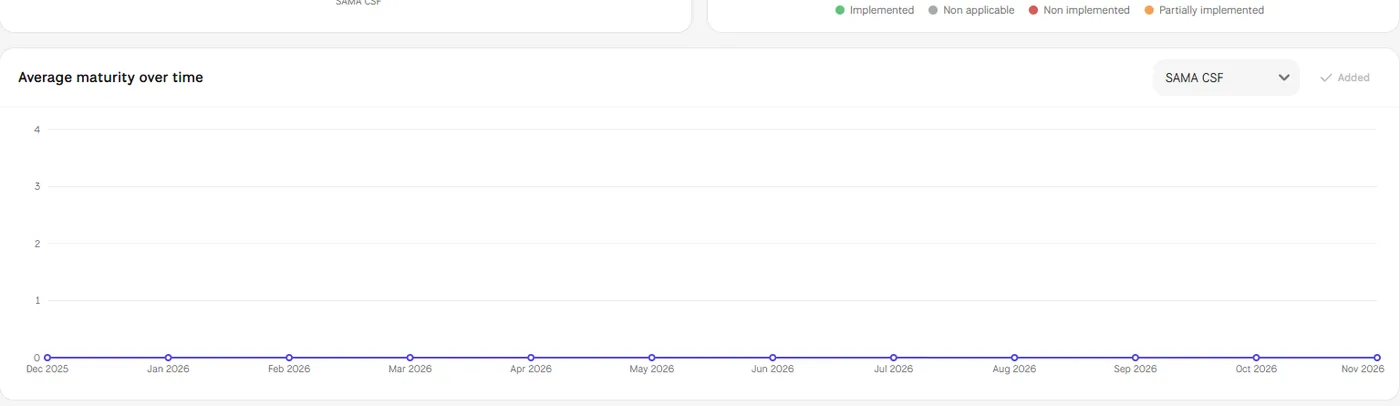
Screens from MUNTABIQ with demo data.
Each control's level comes from one described scale, not from each person's estimate.
The required evidence, the uploaded files and the maturity answer stay on the control page itself.
Average maturity over time shows how the level has moved between assessments on the same framework.
Knows the maturity of the program on the required framework and shows leadership progress backed by evidence.
Spots controls at low levels and sets improvement priorities based on the visible gaps.
Runs the assessment, follows owners' answers and levels, and keeps a log of every change to each control.
The scale in the screenshots is a demo scale of graded levels, each with a description and a percentage. The scale and its level descriptions are set up to suit your organization, and we review them with you during the demo.
Yes. Each assessment runs on a chosen framework and the domains you select from it, and the compliance dashboard shows maturity levels and average maturity over time with a framework selector.
Yes. Each assessment covers a period with a start and due date, and can be closed before a new one starts for the next period. The Average maturity over time chart shows the level month by month, and each control's Activity tab keeps the changes to its answer.
Request a demo and we will show you how control maturity is assessed on the framework you work with, and how we set up the level scale with you.